One open bucket is all it takes. Find it first.
Most cloud breaches start with a setting, not a hack. ConfGoOne reviews exported AWS, Azure and Google Cloud configurations, Terraform files and Kubernetes manifests for public exposure, missing MFA, weak encryption and over-broad permissions — on your own PC.
What ConfGoOne checks
A sample of the real checks in ConfGoOne's rule packs — each one reported with the evidence from your file and the fix.
Nothing leaves your machine
No cloud account connection and no agent — the audit runs on the exported configuration, locally.
Mapped for your auditors
Every finding is mapped to CIS, NIST 800-53, ISO 27001, PCI-DSS and HIPAA.
Fix guidance per provider
Each failure explains the risk and the change to make in that provider's terms.
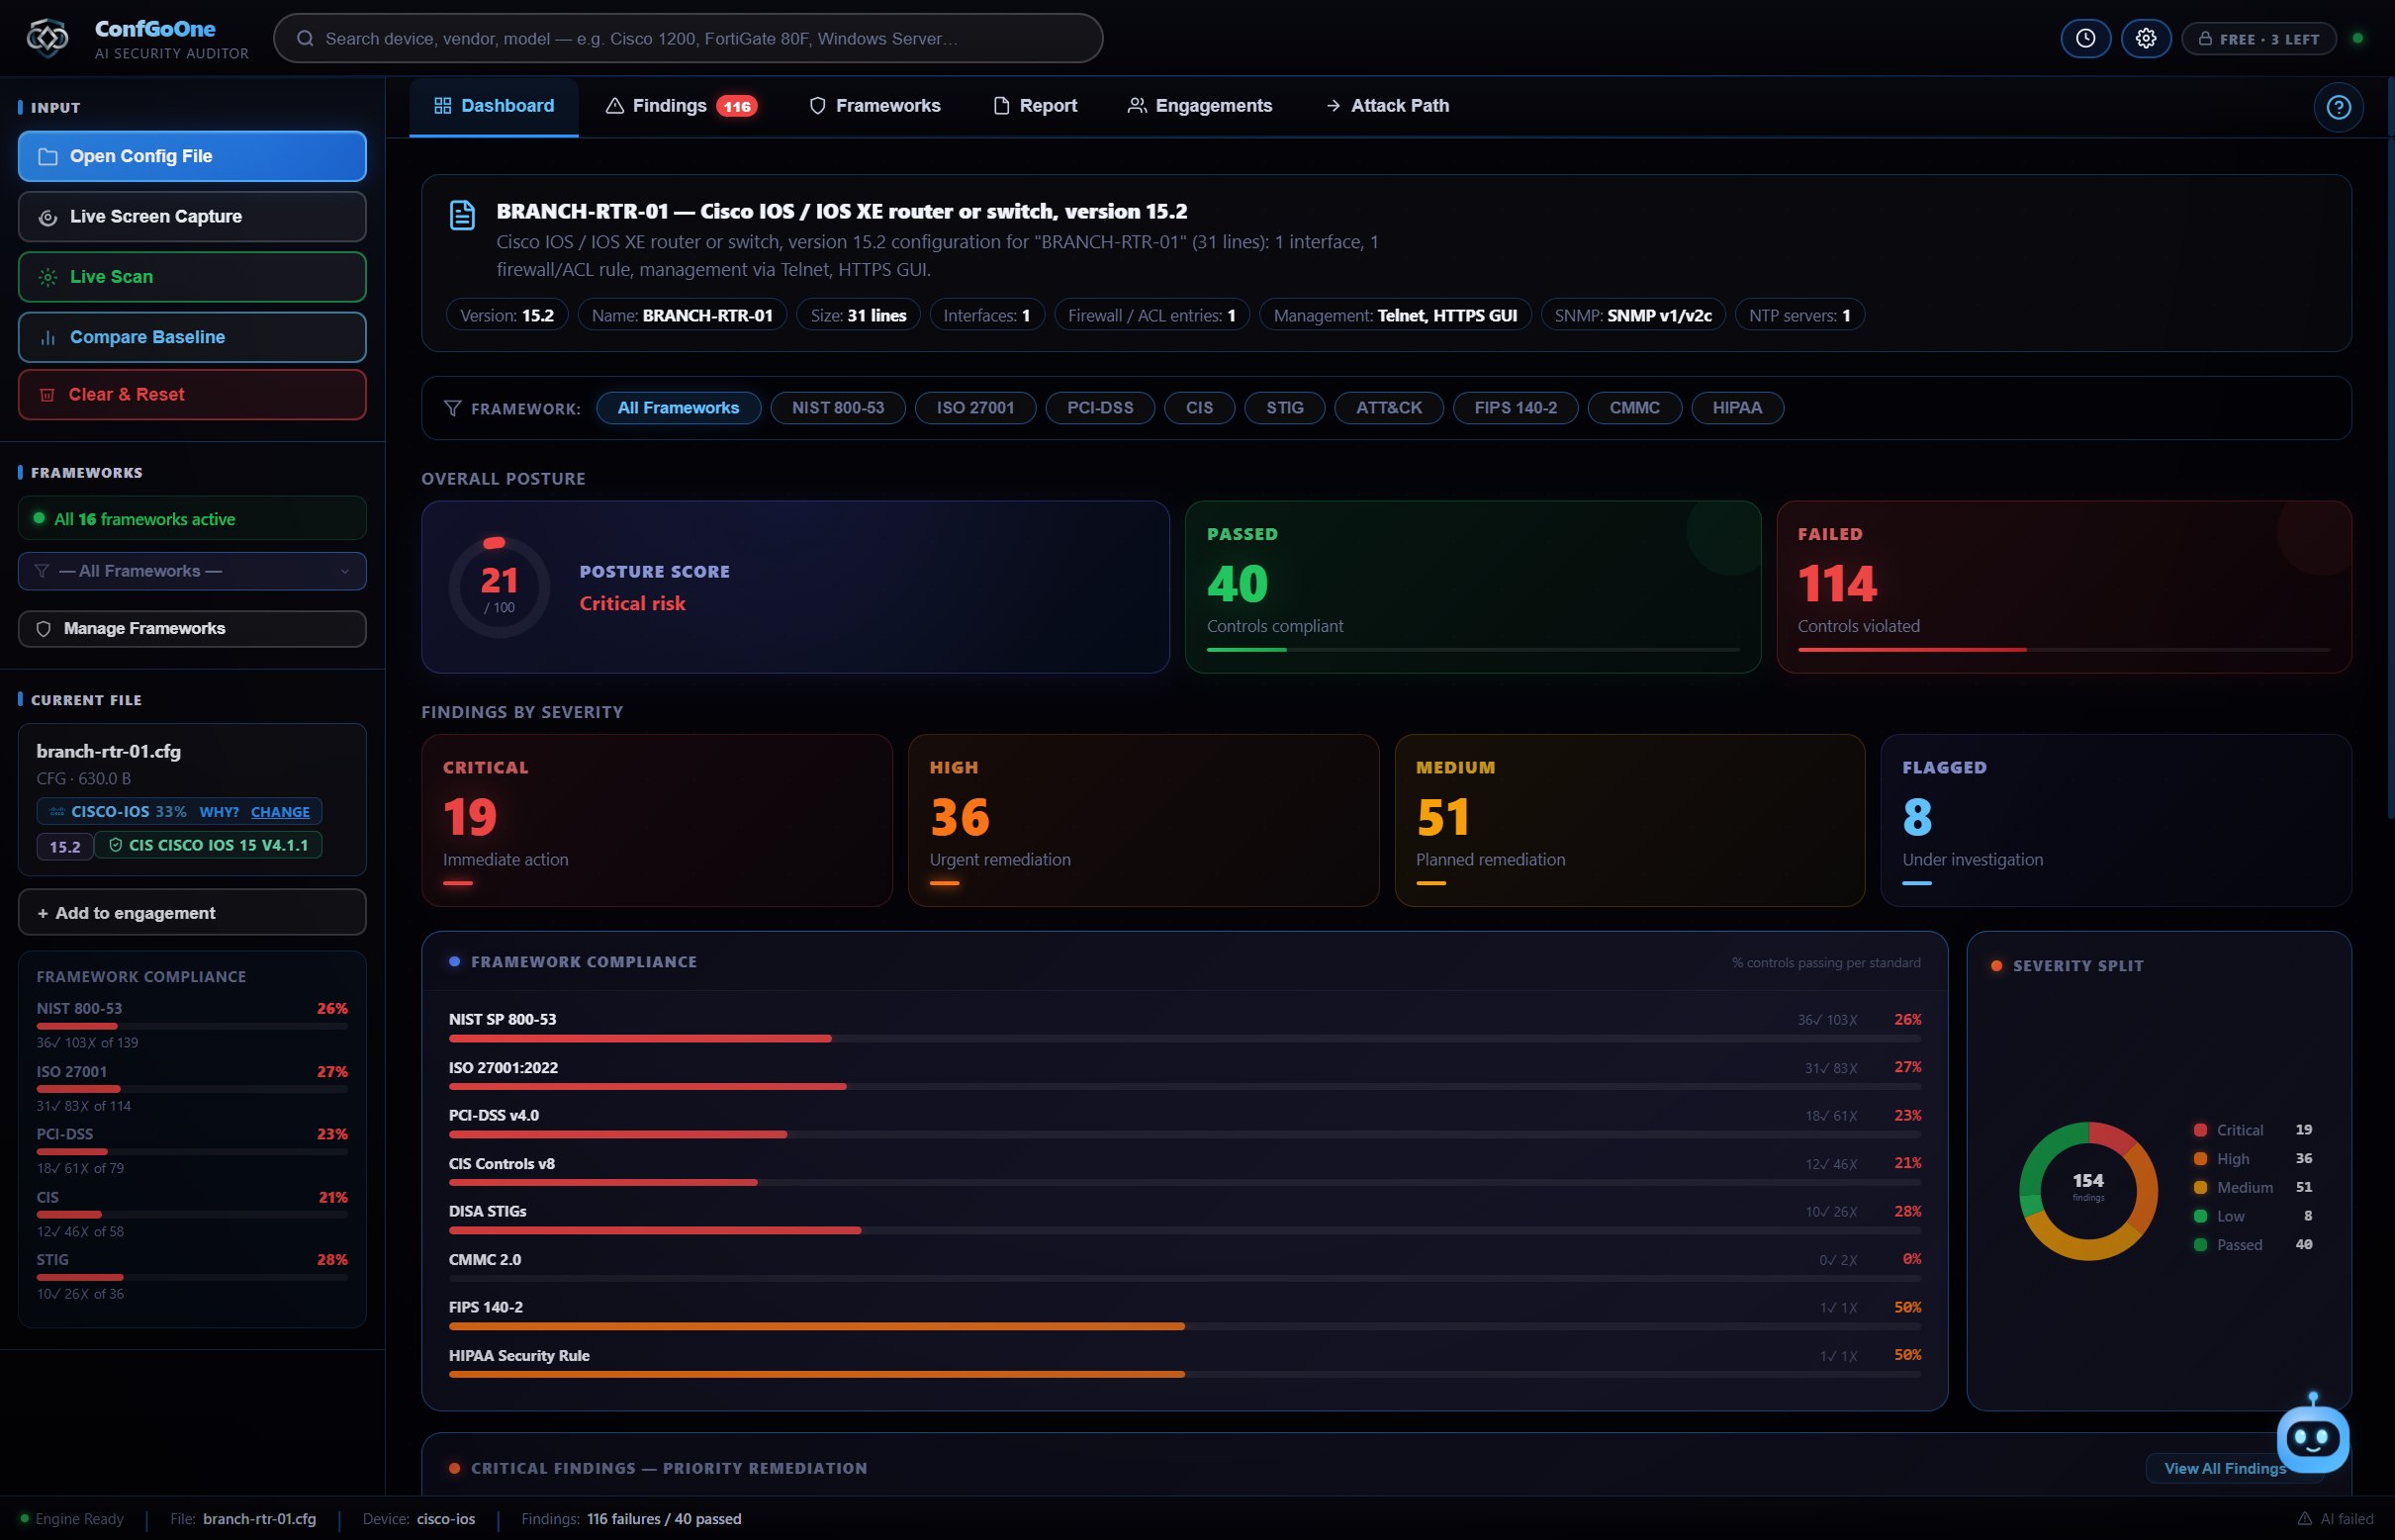
How it works
No setup, no agent, no "start scan" button.
A configuration file, a live connection or a screen capture — whichever you can get.
The device type is recognised and every setting is checked the moment the file opens.
Work through the findings with their fix commands, then export HTML, PDF, Word or a STIG checklist.
Questions
How do I audit an AWS, Azure or GCP configuration?
Export the configuration (or use your Terraform files) and open it in ConfGoOne. It recognises the provider and checks it against its cloud rule pack straight away.
Does ConfGoOne need access to my cloud account?
No. It works from exported configuration files, so no credentials or API access are needed and nothing is sent to the cloud.
Can it audit Terraform before deployment?
Yes. Terraform files can be audited, so misconfigurations are caught before they reach production.
Which compliance frameworks apply to cloud findings?
CIS, NIST SP 800-53, ISO/IEC 27001, PCI-DSS and HIPAA, among others.
Related
Run your first audit in the next minute.
Three free audits. No credit card, no cloud upload — your configs never leave your PC.
Download ConfGoOne →