Hardened servers, proven line by line.
Check Linux and Windows servers, web servers and databases against hardening baselines. ConfGoOne finds weak SSH settings, legacy protocols, missing lockout policies and insecure kernel parameters — and shows the exact change to make.
What ConfGoOne checks
A sample of the real checks in ConfGoOne's rule packs — each one reported with the evidence from your file and the fix.
Baselines you already follow
Findings are mapped to CIS Benchmarks, DISA STIG and NIST SP 800-53.
From finding to fix
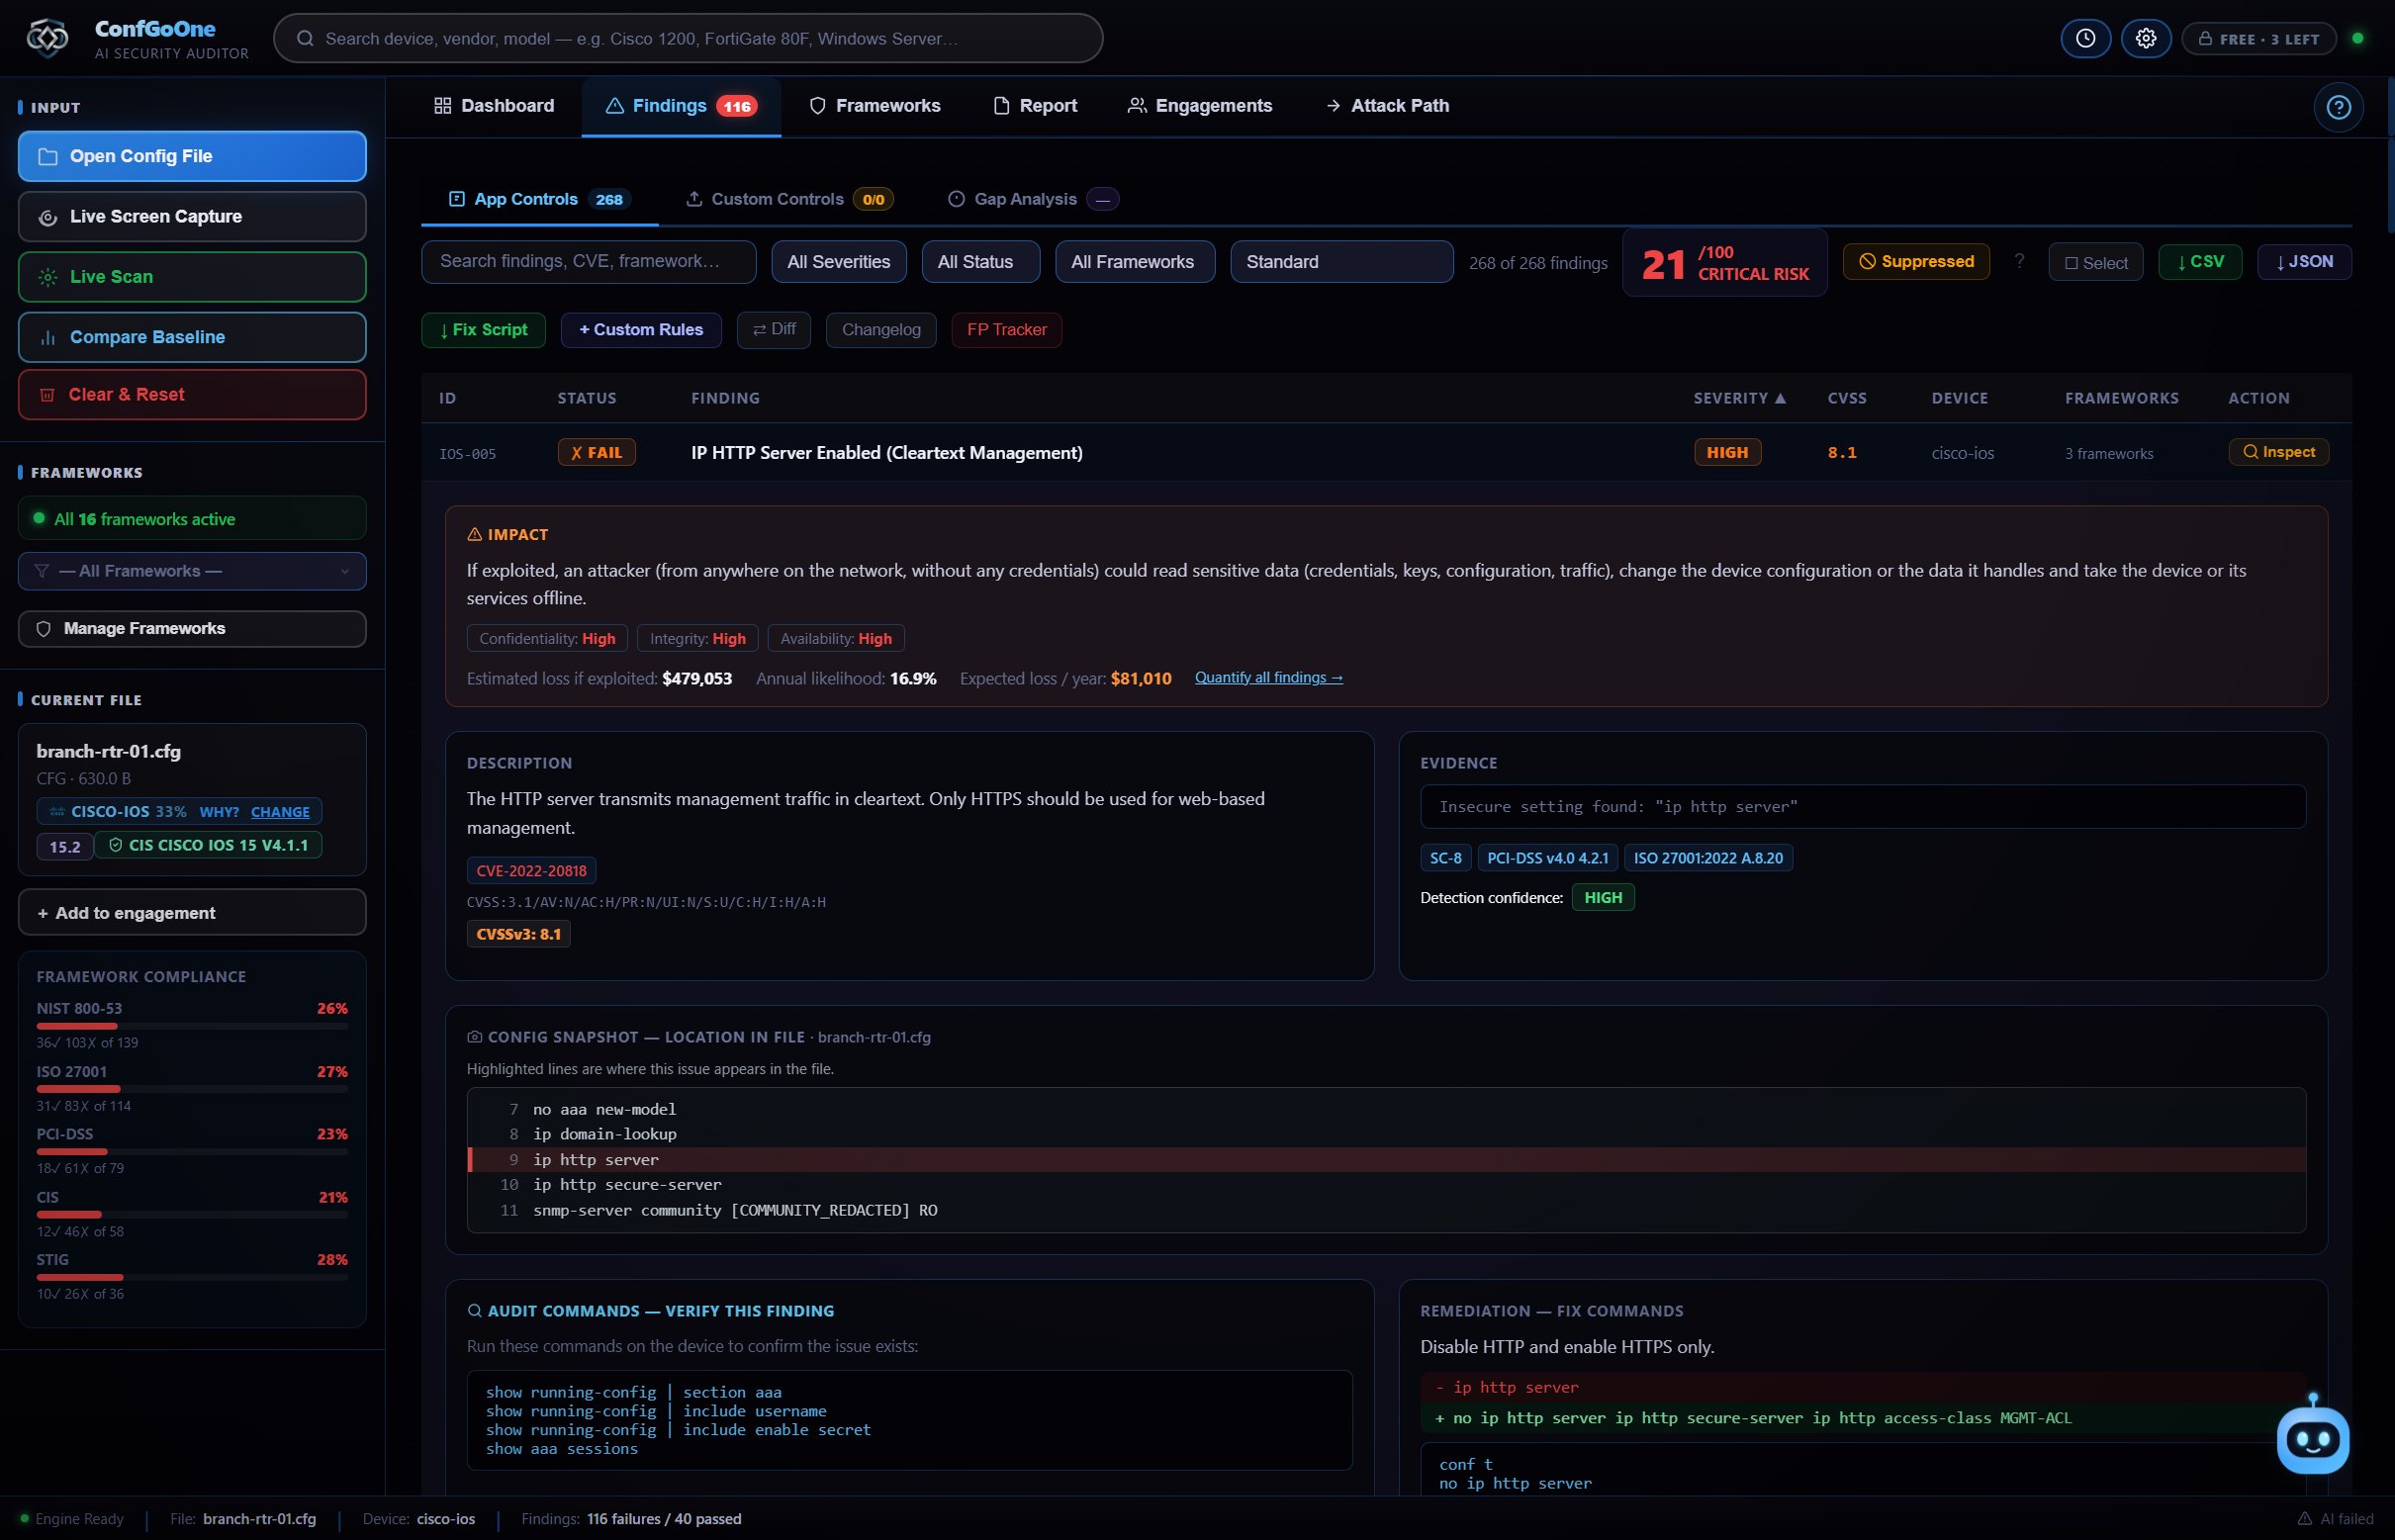
Each failure includes the commands or settings to correct it, plus a Fix Script for all of them.
History and drift
Every audit is kept in History, so you can show a server got more secure over time.
How it works
No setup, no agent, no "start scan" button.
A configuration file, a live connection or a screen capture — whichever you can get.
The device type is recognised and every setting is checked the moment the file opens.
Work through the findings with their fix commands, then export HTML, PDF, Word or a STIG checklist.
Questions
How do I audit Linux server hardening?
Open the relevant configuration (for example sshd_config or sysctl settings) in ConfGoOne. It checks it against hardening rules and shows each issue with the fix.
Can it audit Windows Group Policy?
Yes. Windows security settings and Group Policy exports are checked for issues such as SMBv1, NTLM level, password and lockout policy and RDP settings.
Which web servers and databases are supported?
Apache, Nginx and IIS; MySQL, PostgreSQL and Microsoft SQL Server.
Does it install an agent on my servers?
No. ConfGoOne works from configuration files or a live connection you start — nothing is installed on the server.
Related
Run your first audit in the next minute.
Three free audits. No credit card, no cloud upload — your configs never leave your PC.
Download ConfGoOne →